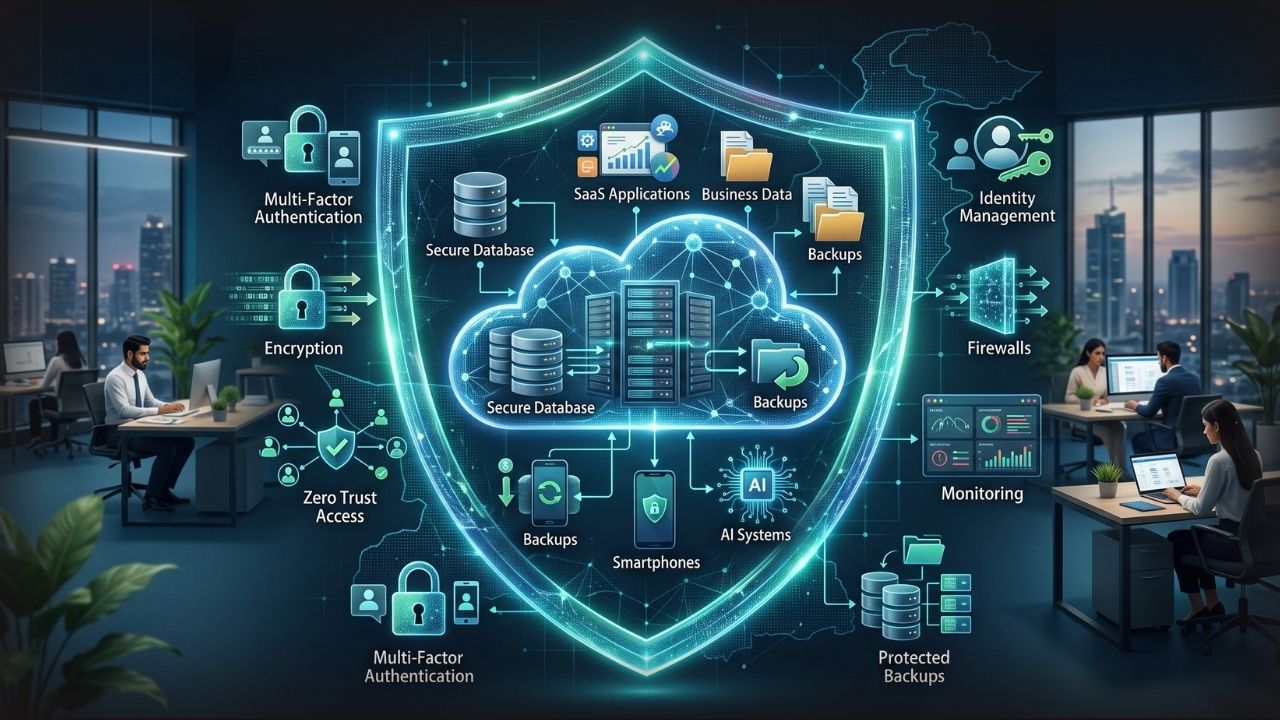
Cloud security is the combination of technologies, policies, processes, and operational practices used to protect cloud accounts, applications, infrastructure, identities, and data against unauthorized access, theft, leakage, malware, ransomware, misconfiguration, and service disruption.
The most important fact in 2026 is that moving data to Amazon Web Services (AWS), Microsoft Azure, Google Cloud, Microsoft 365, Google Workspace, or another reputable cloud provider does not transfer every security responsibility to that provider. Cloud security operates under a shared-responsibility model: the provider secures defined parts of its platform, while customers remain responsible for other controls.
For individuals, that can mean protecting a Google, Microsoft, or Apple account with strong authentication and carefully managing shared files. For a Pakistani business, it can mean implementing identity and access management (IAM), encryption, logging, secure cloud backups, vulnerability management, least privilege, network controls, and an incident-response plan.
AI is adding another layer. Generative AI platforms and autonomous or semi-autonomous agents can access documents, APIs, code, databases, and SaaS systems. Giving those systems excessive permissions creates a new class of cloud risk.
This guide provides 15 practical cloud security measures for 2026, explains cloud security architecture, AWS vs Azure vs Google Cloud controls, SaaS and storage security, backup protection, smartphone access, and the issues businesses in Pakistan should evaluate.
What Is Cloud Security?
Cloud security protects cloud-hosted data, applications, user accounts, virtual machines, storage, APIs, databases, networks, SaaS applications, and administrative systems.
An effective cloud security baseline includes:
- Phishing-resistant MFA where practical
- Least-privilege access
- Strong identity management
- Secure configuration
- Encryption
- Protected secrets and cryptographic keys
- Logging and monitoring
- Vulnerability and patch management
- Secure APIs
- Network controls
- Endpoint protection
- Independent backups
- Incident response
- Regular access reviews
- Continuous security testing
The central principle is simple: trust should be earned through identity, device, context, and policy rather than assumed because a user or system appears to be “inside” a corporate network.
The NIST Zero Trust Architecture provides an authoritative framework for this approach.
For cloud fundamentals first, IT Magazine Pakistan’s cloud computing guide for Pakistan explains SaaS, PaaS, IaaS, public cloud, private cloud, and hybrid architecture.
Key Takeaways
Cloud security is a shared responsibility. AWS, Microsoft, Google, and SaaS providers can secure infrastructure, but customers still need to secure identities, data, configurations, endpoints, and many application layers.
Identity has become a primary security perimeter. One compromised administrator account can expose storage, databases, AI resources, customer information, and backups.
MFA is essential, but not all MFA methods provide equal phishing resistance. Passkeys and FIDO2 security keys can offer stronger protection against credential phishing than SMS codes.
Cloud backup needs separate protection. Attackers increasingly attempt to compromise recovery systems as part of ransomware incidents.
Encryption protects data, but key management determines who can decrypt it.
And security configuration should be monitored continuously. Cloud environments change too quickly for an annual security review to be sufficient on its own.
Table of Contents
Cloud Security Comparison Table
| Security layer | Main risk | Important control |
| Identity | Stolen credentials | MFA/passkeys + least privilege |
| Cloud storage | Public data exposure | Private-by-default permissions |
| Administrators | Account takeover | Privileged-access controls |
| Data | Unauthorized disclosure | Encryption + classification |
| APIs | Unauthorized requests | Authentication + authorization |
| Virtual machines | Exploitation | Patching + hardening |
| SaaS | Data leakage | Access controls + configuration |
| Backups | Ransomware/deletion | Isolation + immutable retention |
| Endpoints | Stolen sessions | Device security |
| Logs | Undetected attacks | Central monitoring |
| AI agents | Excessive actions | Minimum permissions + audit |
| Secrets | Credential theft | Secrets-management platform |
No single tool protects all of these layers.
15 Essential Cloud Security Tips for 2026
1. Protect Every Important Account With Strong MFA
Passwords alone are not adequate protection for privileged cloud accounts.
If an attacker obtains a password through phishing, credential stuffing, malware, or reuse from another breach, multi-factor authentication provides another barrier.
However, MFA methods are not equally strong.
SMS and one-time codes can improve security substantially over passwords alone, but phishing-resistant methods such as FIDO2 security keys and passkeys are preferable for high-value administrator accounts where supported.
The U.S. Cybersecurity and Infrastructure Security Agency’s MFA guidance recommends stronger MFA approaches, particularly phishing-resistant methods.
For individuals and small teams, IT Magazine Pakistan’s password security guide explains how passwords, password managers, and MFA fit together.
2. Follow the Principle of Least Privilege
A user should have only the permissions required for their job.
The same rule applies to applications, virtual machines, service accounts, APIs, and AI agents.
An employee who only reads reports does not need database-administrator permissions.
A web application that reads objects from one storage bucket does not need permission to delete every company’s backup.
Overprivileged accounts expand the blast radius of a compromise.
Cloud security teams should periodically review privileges and remove unnecessary permissions.
Temporary elevated access is preferable to permanent administrator privileges where the platform and workflow support it.
3. Secure Root and Highest-Privilege Accounts Aggressively
Cloud platforms contain accounts or roles capable of making extremely sensitive changes.
Treat these identities differently from ordinary user accounts.
Do not use the highest-privilege account for routine administration.
Protect it with the strongest available authentication.
Restrict access.
Monitor its use.
Secure recovery methods.
Store emergency credentials appropriately.
One compromised cloud super-admin can potentially change permissions, create new credentials, access sensitive data, disable security tooling, and interfere with recovery systems.
Administrative convenience should never outweigh that risk.
4. Encrypt Sensitive Data
Encryption should protect appropriate data both while it travels across networks and while it is stored.
Transport Layer Security (TLS) is commonly used to protect data in transit.
Cloud platforms also provide encryption at rest for storage, databases, disks, and other services.
For high-security scenarios, organizations may require customer-managed encryption keys rather than relying entirely on provider-managed keys.
That additional control comes with additional responsibility.
Lose a critical customer-controlled key and the organization may lose the ability to decrypt its own information.
Key rotation, permissions, backup, lifecycle management, and recovery procedures therefore matter.
5. Keep Secrets Out of Source Code
API keys, database passwords, private keys, cloud access credentials, and AI service tokens should not be embedded directly in public or shared source code.
Once a secret enters a Git repository, deleting it from the latest version may not remove it from repository history.
Use dedicated secrets-management services where appropriate.
AWS, Azure, and Google Cloud all provide technologies for protecting application secrets and cryptographic material.
Also use short-lived credentials instead of permanent keys when architecture allows it.
If a secret is accidentally exposed, revoke and rotate it. Do not merely delete the visible copy and assume the threat is gone.
6. Configure Cloud Storage as Private by Default
Cloud storage misconfiguration has caused numerous high-profile data exposures.
Storage containing customer documents, backups, logs, source files, or business records should not be publicly accessible unless public access is explicitly required.
Review:
- Bucket or container policies
- Object permissions
- Public-access settings
- Sharing links
- Anonymous access
- Cross-account permissions
- Storage logs
- Expiration rules
Public website assets and private customer records should not be casually mixed under the same access model.
IT Magazine Pakistan’s cloud storage comparison explains the difference between consumer products such as Google Drive and infrastructure storage such as Amazon S3, Azure Blob Storage, and Google Cloud Storage.
7. Enable Logging Before You Need It
Security incidents are much harder to investigate when nobody recorded what happened.
Configure appropriate audit logs for administrator activity, authentication, storage access, security changes, and critical applications.
Then protect those logs.
An attacker who can alter production systems should not automatically be able to erase every copy of the audit trail.
Logs also require monitoring.
Collecting terabytes of logs that nobody reviews does not provide meaningful detection.
Organizations should establish alerts around suspicious events such as privileged-role creation, disabled security controls, unusual authentication, unexpected data access, or attempts to modify backup policies.
8. Patch Systems You Still Manage
Managed cloud services can reduce patching responsibilities, but Infrastructure as a Service does not eliminate them.
If your organization operates a virtual machine on AWS EC2, Azure Virtual Machines, or Google Compute Engine, it may remain responsible for patching and hardening the guest operating system and applications.
Unpatched internet-facing software can be exploited regardless of how secure the provider’s physical data center is.
Maintain an inventory of systems, automate patching where suitable, monitor vulnerability information, and retire unsupported operating systems.
The provider cannot patch applications it does not control.
9. Segment Networks and Minimize Internet Exposure
Not every server needs a public IP address.
Databases, internal services, management interfaces, and backend systems can often operate through private networking.
Network segmentation limits direct exposure and can reduce an attacker’s freedom of movement after compromise.
Use security groups, cloud firewalls, private endpoints, virtual networks, subnet controls, and application-layer protection according to architecture.
Avoid building a “hard shell, soft center” network where anything that crosses one firewall receives unrestricted access.
Modern cloud security combines network boundaries with identity-aware access.
10. Protect Cloud Backups From Attackers
Backups are a security control, but only if they survive the incident.
Ransomware operators may attempt to delete backups before encrypting production systems.
Use separate or tightly restricted backup credentials and protect administrative actions with MFA.
For critical workloads, evaluate immutable retention or write-once protection where appropriate.
Maintain multiple recovery points and test restoration regularly.
The CISA ransomware guidance recommends maintaining protected backup copies and testing recovery.
IT Magazine Pakistan’s cloud backup guide provides a complete backup architecture, while its ransomware explainer covers the threat itself.
11. Secure APIs, Not Just Websites
Modern cloud applications depend heavily on APIs.
A web page can look perfectly protected while an underlying API exposes customer data because authorization was implemented incorrectly.
Every API request should receive appropriate authentication and authorization.
Validate input.
Apply rate controls where relevant.
Keep API credentials out of client-side code when they need to remain secret.
Log sensitive operations.
Test for broken object-level authorization and other API-specific vulnerabilities.
The OWASP API Security Project is a useful authoritative industry reference for common API risks.
12. Secure Employee Devices
Cloud security does not stop at the cloud provider.
If an administrator logs into Azure from a laptop infected with credential-stealing malware, the endpoint can undermine strong server-side security.
Business devices should use current operating-system versions, disk encryption, endpoint protection, automatic security updates, strong screen locking, and appropriate device-management controls.
Mobile access matters too.
Samsung, Google Pixel, Xiaomi, Oppo, Vivo, Realme, Infinix, and Tecno Android phones can access SaaS dashboards, Google Workspace, cloud drives, and administrative systems. Apple iPhones can do the same.
The fact that a modern Snapdragon or MediaTek device supports 5G or has an AMOLED screen says nothing about account security.
Keep Android, Google Play system components, manufacturer patches, and iOS up to date.
IT Magazine Pakistan’s mobile security guide covers this endpoint layer.
13. Secure SaaS Applications Separately
Using Software as a Service does not mean the customer has zero security responsibility.
Consider Google Workspace or Microsoft 365.
The provider protects the underlying service, but an organization still controls many aspects of user identities, sharing, application integrations, administrator roles, data governance, and device access.
Review third-party OAuth permissions.
Remove former employees quickly.
Disable abandoned accounts.
Restrict external sharing where necessary.
Investigate whether the application’s native retention meets your recovery requirements.
IT Magazine Pakistan’s SaaS explained guide covers the customer/provider division in greater detail.
14. Treat AI Agents as Privileged Users
AI is changing cloud security in 2026.
An ordinary chatbot produces responses. An agentic system may have permission to call APIs, search corporate documents, modify CRM data, create tickets, execute code, or initiate workflows.
That makes permissions critical.
Do not give an AI agent administrator access because it makes development easier.
Give the agent the minimum tools and data required for its role.
Log important actions.
Require human approval for sensitive or irreversible operations where appropriate.
Protect against prompt injection and untrusted data attempting to manipulate the agent.
Separate high-risk capabilities.
IT Magazine Pakistan’s guide to AI agents and the changing workplace provides more context for this rapidly developing area.
15. Build and Test an Incident-Response Plan
No security architecture guarantees that an incident will never happen.
A mature organization plans for failure.
Your incident-response process should answer practical questions:
Who receives the first alert?
Who has authority to disable a compromised account?
How are cloud access keys revoked?
How are affected systems isolated?
Where are logs stored?
Who communicates with customers?
How are backups restored?
Who contacts the provider?
How does the organization operate if the primary cloud environment is temporarily inaccessible?
Test the process with tabletop exercises.
The first time the team discusses ransomware should not be during an active ransomware incident.
The NIST Cybersecurity Framework provides a widely used structure for cybersecurity risk management.
The Cloud Shared-Responsibility Model Explained
One of the most important cloud security concepts is the difference between “security of the cloud” and “security in the cloud.”
The exact language and boundary differ by provider and service, but the principle is consistent.
The provider typically handles physical facilities, core networking, hardware, and other underlying infrastructure layers.
The customer’s responsibilities increase as they gain more infrastructure control.
SaaS
The provider manages most of the application stack.
The customer generally focuses on identities, access, data, endpoints, sharing, and application configuration.
PaaS
The provider manages infrastructure and more of the application platform.
Customers manage their application code, data, permissions, and relevant configurations.
IaaS
Customers gain more flexibility but are responsible for substantially more, often including guest operating systems, applications, firewall rules, identities, and data.
For background, cloud security encompasses these controls across public, private, and hybrid environments.
AWS vs Azure vs Google Cloud Security
AWS, Microsoft Azure, and Google Cloud all provide extensive enterprise security capabilities.
| Security area | AWS | Azure | Google Cloud |
| Identity | AWS IAM | Microsoft Entra ID + Azure RBAC | Cloud IAM |
| Key management | AWS KMS | Azure Key Vault | Cloud KMS |
| Secrets | Secrets Manager | Key Vault | Secret Manager |
| Security posture | Security Hub ecosystem | Defender for Cloud | Security Command Center |
| DDoS protection | AWS Shield | Azure DDoS Protection | Cloud Armor/network capabilities |
| Logging | CloudTrail/CloudWatch | Azure Monitor/Activity Logs | Cloud Audit Logs/Observability |
This table is simplified. The providers have significantly broader security portfolios.
None is automatically secure simply because the tools exist.
A badly configured AWS account can be exposed. The same is true of Azure or Google Cloud.
Provider selection should instead consider architecture, existing identity systems, required compliance certifications, region availability, staff expertise, service integrations, support, and total cost.
IT Magazine Pakistan’s AWS vs Azure vs Google Cloud comparison examines these broader trade-offs.
Cloud Storage Security
Consumer cloud drives and enterprise object storage require different security approaches.
Google Drive, OneDrive and iCloud
For individuals, focus on account security.
Use strong authentication, review active sessions, protect recovery methods, and audit shared links periodically.
A document can be perfectly encrypted by the platform and still leak because someone created a public sharing link.
Amazon S3, Azure Blob Storage and Google Cloud Storage
For business infrastructure, use explicit access policies.
Keep sensitive storage private, log access, encrypt appropriate content, and separate public assets from confidential information.
Review cross-account access and application credentials.
Data lifecycle rules should also be tested carefully before allowing automated deletion.
Cloud Backup Security and the 3-2-1 Rule
Cloud security should include recovery.
The traditional 3-2-1 backup strategy recommends three copies of important data, on two types of storage or media, with at least one copy off-site.
Modern ransomware-conscious variants add immutable or offline protection and backup verification.
The principle matters more than the slogan: one compromise should not be capable of destroying every recovery copy.
Cloud redundancy alone does not solve accidental deletion.
If a database change is replicated immediately across three availability zones, you may now have three perfectly synchronized copies of the same unwanted change.
Backup provides historical recovery. Redundancy provides availability.
They solve different problems.
Cloud Security for Pakistani Businesses
Cloud adoption can be valuable for companies in Karachi, Lahore, Islamabad, Rawalpindi, Faisalabad, Multan, Peshawar, Quetta, and elsewhere in Pakistan, but security planning should consider local realities.
Data location
Identify where sensitive information is stored, processed, and backed up.
Different sectors may have regulatory requirements affecting data handling.
Financial institutions should consult current State Bank of Pakistan information where applicable, while organizations dealing with telecommunications matters may need to review relevant Pakistan Telecommunication Authority resources.
Specific legal questions require qualified professional advice.
Internet reliability
Cloud access depends heavily on connectivity.
Businesses with critical cloud workloads may need redundant ISP connections, tested failover, and procedures for connectivity outages.
Skills
A cloud environment is only as secure as the people configuring it.
Invest in IAM, networking, Linux or Windows administration, logging, cloud architecture, incident response, infrastructure as code, and secure software-development skills.
Foreign-currency costs
International cybersecurity and cloud services may be invoiced in foreign currencies.
PKR exchange-rate movements can affect the real cost of security tooling and cloud infrastructure, so long-term budgets should account for that risk.
Step-by-Step Cloud Security Checklist
Step 1: Inventory your cloud
Identify AWS accounts, Azure subscriptions, Google Cloud projects, SaaS applications, cloud drives, AI services, and administrative users.
You cannot protect systems nobody knows exist.
Step 2: Classify data
Determine what is public, internal, confidential, regulated, or business-critical.
Step 3: Secure identity
Require appropriate MFA, eliminate shared administrator accounts, and apply least privilege.
Step 4: Remove exposed resources
Audit public storage, firewall rules, databases, dashboards, and administration interfaces.
Step 5: Centralize logs
Ensure important activity is retained and monitored.
Step 6: Protect secrets
Move credentials from code and spreadsheets into proper secret-management systems.
Step 7: Patch and scan
Patch customer-managed systems and scan for vulnerabilities and misconfigurations.
Step 8: Secure backups
Separate permissions and test recovery.
Step 9: Review SaaS and AI integrations
Remove unnecessary applications, OAuth grants, API keys, and agent permissions.
Step 10: Test incident response
Simulate a stolen administrator credential, ransomware event, or exposed database.
Document what fails and improve it.
Cloud Security Pros and Cons
Advantages
Major cloud providers offer sophisticated identity platforms, encryption, logging, threat detection, physical data-center security, resilient infrastructure, managed security products, automated policy enforcement, and rapid patching of provider-managed services.
Smaller businesses can access security technologies that would be difficult to build independently.
Limitations
Cloud environments are complex.
A single IAM policy can expose enormous resources.
Costs for logging and security tooling can grow.
Organizations also depend on provider availability and correct configuration.
Misconfiguration, phishing, insecure applications, excessive privileges, unmanaged SaaS usage, and poor backup design remain customer risks.
Cloud can provide excellent security capabilities without automatically producing a secure organization.
Common Cloud Security Mistakes
The most common mistake is assuming the cloud provider handles everything.
Another is giving every developer broad administrator privileges.
Businesses also expose sensitive storage accidentally, leave unused credentials active, embed secrets in source code, ignore logs, or fail to revoke departing employees promptly.
Overlooking recovery is another serious problem.
An organization can have sophisticated detection systems yet still struggle after ransomware because nobody tested the backups.
Do not focus exclusively on preventing attacks. Build resilience for when prevention fails.
Expert Tips for Cloud Security in 2026
Use separate production and non-production environments where practical.
Centralize identity and avoid unmanaged cloud accounts created on personal email addresses.
Prefer short-lived credentials and federated identity over permanent access keys where the architecture supports them.
Protect high-value administrators with phishing-resistant MFA.
Build security controls into infrastructure-as-code templates so developers receive safer defaults automatically.
Set budgets for security logging rather than disabling logs because they cost money.
Review AI permissions with the same seriousness as human administrator permissions.
Finally, measure recovery. Time how long it takes to restore a critical system. Real data is much more useful than assuming the backup will be fast enough.
Buying Advice: How to Choose Cloud Security Tools
Do not start with a vendor.
Start with the problem.
A company struggling with phishing may need identity improvements before buying another network scanner.
A business with dozens of exposed cloud resources may benefit from cloud-security posture management and better infrastructure policies.
A company worried about ransomware needs protected backup and incident response as well as endpoint security.
Check whether your existing AWS, Azure, Google Cloud, Microsoft 365, or Google Workspace licensing already provides capabilities you have not configured.
Then evaluate third-party tools where genuine gaps remain.
During purchasing, consider deployment effort, integration, alert quality, staff skills, regional support, data location, API access, pricing, and exit options.
A tool that produces 10,000 alerts nobody investigates is not effective cloud security.
Frequently Asked Questions
What is cloud security?
Cloud security is the set of technologies, policies, configurations, and operational practices used to protect cloud accounts, infrastructure, applications, identities, and data from unauthorized access, attack, loss, and disruption.
What is the biggest cloud security risk?
There is no single risk for every organization, but compromised identities, excessive permissions, misconfiguration, exposed credentials, insecure applications, and inadequate recovery controls are major concerns.
Is cloud computing safer than storing data locally?
Either can be secure or insecure. Major cloud providers offer advanced security capabilities, but customers must configure them correctly. Local environments provide more direct control but also require organizations to secure and maintain the entire infrastructure.
Is AWS more secure than Azure or Google Cloud?
There is no useful universal security winner. AWS, Azure, and Google Cloud all provide mature security capabilities. Actual security depends heavily on architecture, identity controls, application design, customer configuration, staff expertise, and operational processes.
Does encryption make cloud data completely safe?
No. Encryption protects data under defined conditions, but compromised user accounts, stolen keys, insecure applications, malicious insiders, or incorrect permissions can still expose information.
What is zero-trust cloud security?
Zero trust avoids automatically trusting a user or device merely because of its network location. Access decisions consider identity, permissions, device state, context, and policy, with continuous verification where appropriate.
Why is MFA important for cloud accounts?
A password can be stolen through phishing or malware. MFA requires another authentication factor, making a stolen password less useful. Phishing-resistant methods are preferable for high-value accounts when supported.
Is Google Drive safe for sensitive files?
Google provides strong security capabilities, but whether Drive is appropriate depends on the sensitivity of the information, account security, sharing settings, organizational controls, encryption requirements, and applicable regulations.
How do I protect cloud backups from ransomware?
Use tightly restricted backup permissions, strong MFA, multiple recovery points, separate security boundaries, and immutable or protected copies where appropriate. Test restoration regularly.
What cloud security should a small Pakistani business implement first?
Start with an inventory, strong MFA, least-privilege access, secure backups, software updates, endpoint protection, private storage settings, centralized administration, and an incident-response plan. Add specialized tooling according to measured risk.
Conclusion
Cloud security in 2026 is fundamentally about controlling trust.
Your data may reside in Amazon Web Services, Microsoft Azure, Google Cloud, Google Workspace, Microsoft 365, iCloud, or dozens of SaaS applications, but the same principles continue to matter: verify identities, minimize permissions, encrypt sensitive information, protect credentials, monitor important actions, patch what you control, secure backups, and prepare for incidents.
The shared-responsibility model is especially important. A provider can operate highly secure data centers while a customer accidentally exposes a database or grants administrator access to a compromised account.
AI makes these controls even more important. AI agents capable of interacting with cloud applications should receive carefully limited permissions, comprehensive logging, and human approval around high-impact actions.
For organizations in Pakistan, effective cloud security also requires local planning. Understand internet dependencies, data-location requirements, regulatory obligations, support arrangements, and the PKR cost of international security tools.
Start with identity and recovery. Protect administrator accounts with strong MFA, enforce least privilege, keep independent and tested backups, and make sure security logs exist before an incident occurs.
The strongest cloud security program is not the one with the most products. It is the one that knows what it owns, limits who and what can access it, detects unusual activity, and can recover when something still goes wrong.